Zero trust security is often discussed as if it requires a large enterprise security program. In practice, many of its core principles are highly relevant to small businesses using Microsoft 365, Google Workspace, SaaS applications, cloud hosting, remote workers and contractors.
The central idea is simple: access should not be trusted automatically just because a person or device is inside a company network. Identity, device state, application, resource sensitivity and business context should influence access decisions.
What Is Zero Trust Security?
Zero trust is a security approach that assumes access should be explicitly verified rather than automatically trusted. A user who successfully connects to a company network should not automatically gain broad access to every internal resource.
Instead, organizations evaluate who is requesting access, which device is being used, what resource is requested, what level of privilege is required and whether the request matches expected behavior.
Why Zero Trust Matters More to Small Businesses in 2026
Many small businesses no longer operate from one protected office network. Employees use home broadband, mobile devices, cloud applications, collaboration platforms, remote-access tools and third-party SaaS services.
Common small-business conditions that support a zero-trust approach
- Remote or hybrid employees.
- Contractors needing temporary access.
- Microsoft 365 or Google Workspace.
- Cloud accounting and CRM platforms.
- Web-based administrative tools.
- Multiple SaaS applications.
- Personal or unmanaged devices.
- Distributed cloud infrastructure.
Zero Trust Is Not a Single Product
Businesses should be cautious of marketing that presents zero trust as one software license. Implementation normally involves several controls working together, including identity, endpoint security, access policy, logging and data protection.
10 Zero Trust Principles Small Businesses Can Apply
1. Verify identity for every important access request
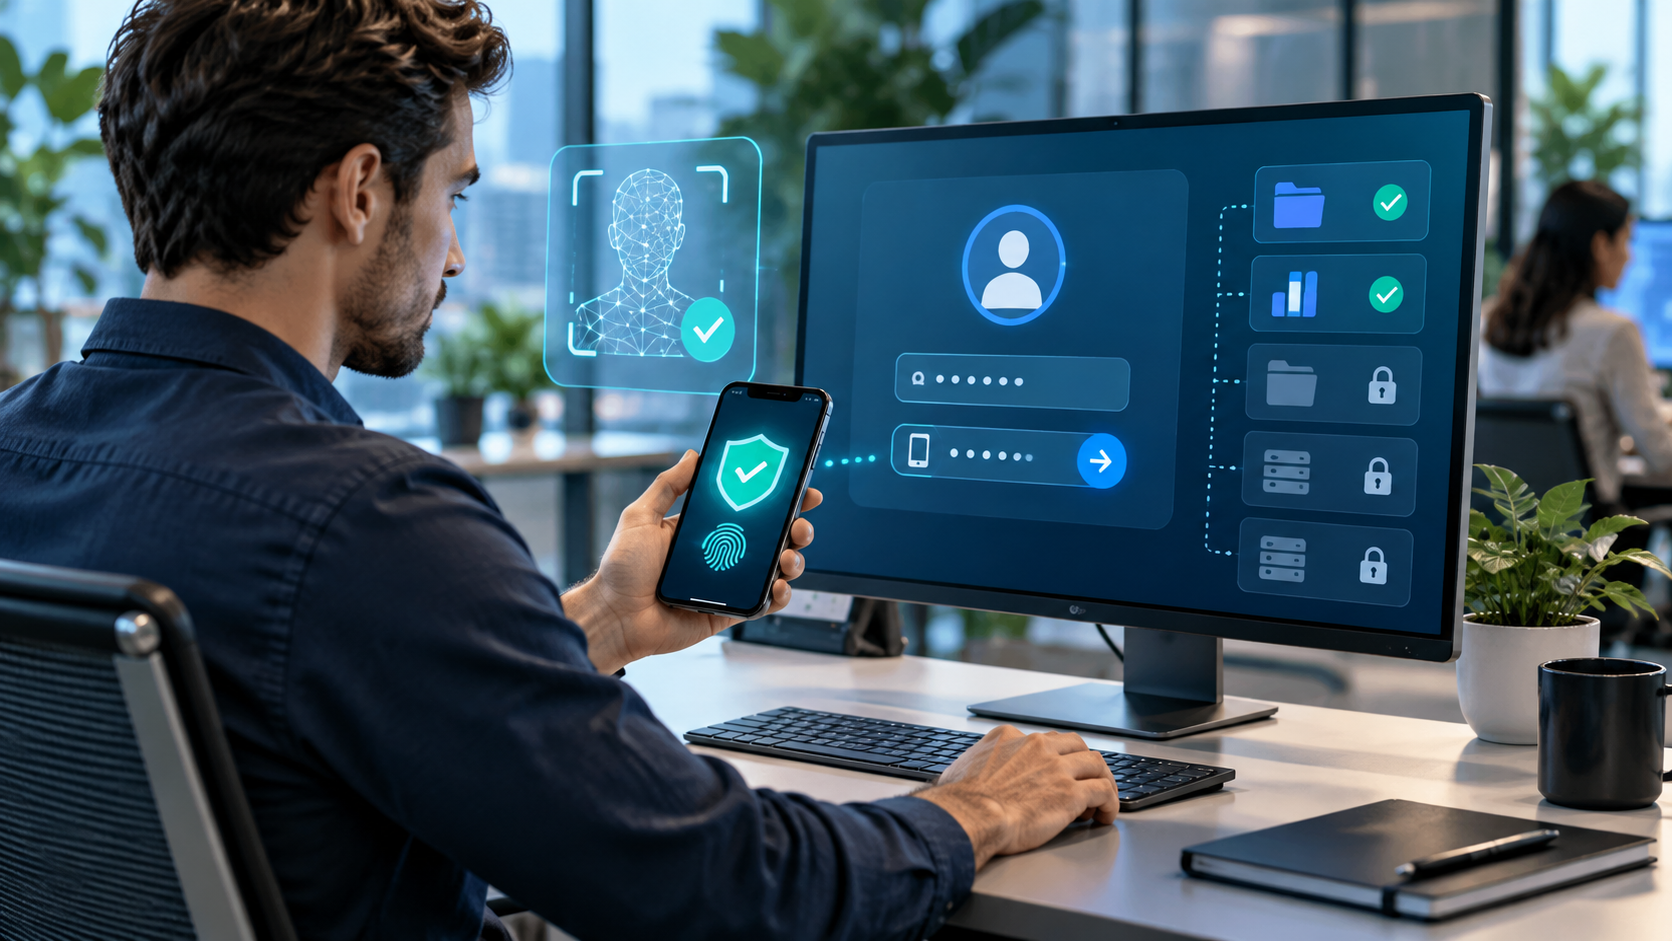
Use strong authentication for email, cloud administration, finance systems, hosting, DNS and other critical services.
2. Prefer phishing-resistant authentication
Passwords and SMS codes can be phished. Passkeys and hardware-backed authentication can provide stronger resistance. See our passkeys vs passwords comparison.
3. Give users only the access they need
Least privilege limits the damage caused by mistakes or compromised accounts.
4. Protect administrator accounts separately
Privileged accounts should receive stronger controls and should not be used casually for everyday browsing or email.
5. Consider device trust
Access decisions should consider whether a device is supported, patched, encrypted and protected.
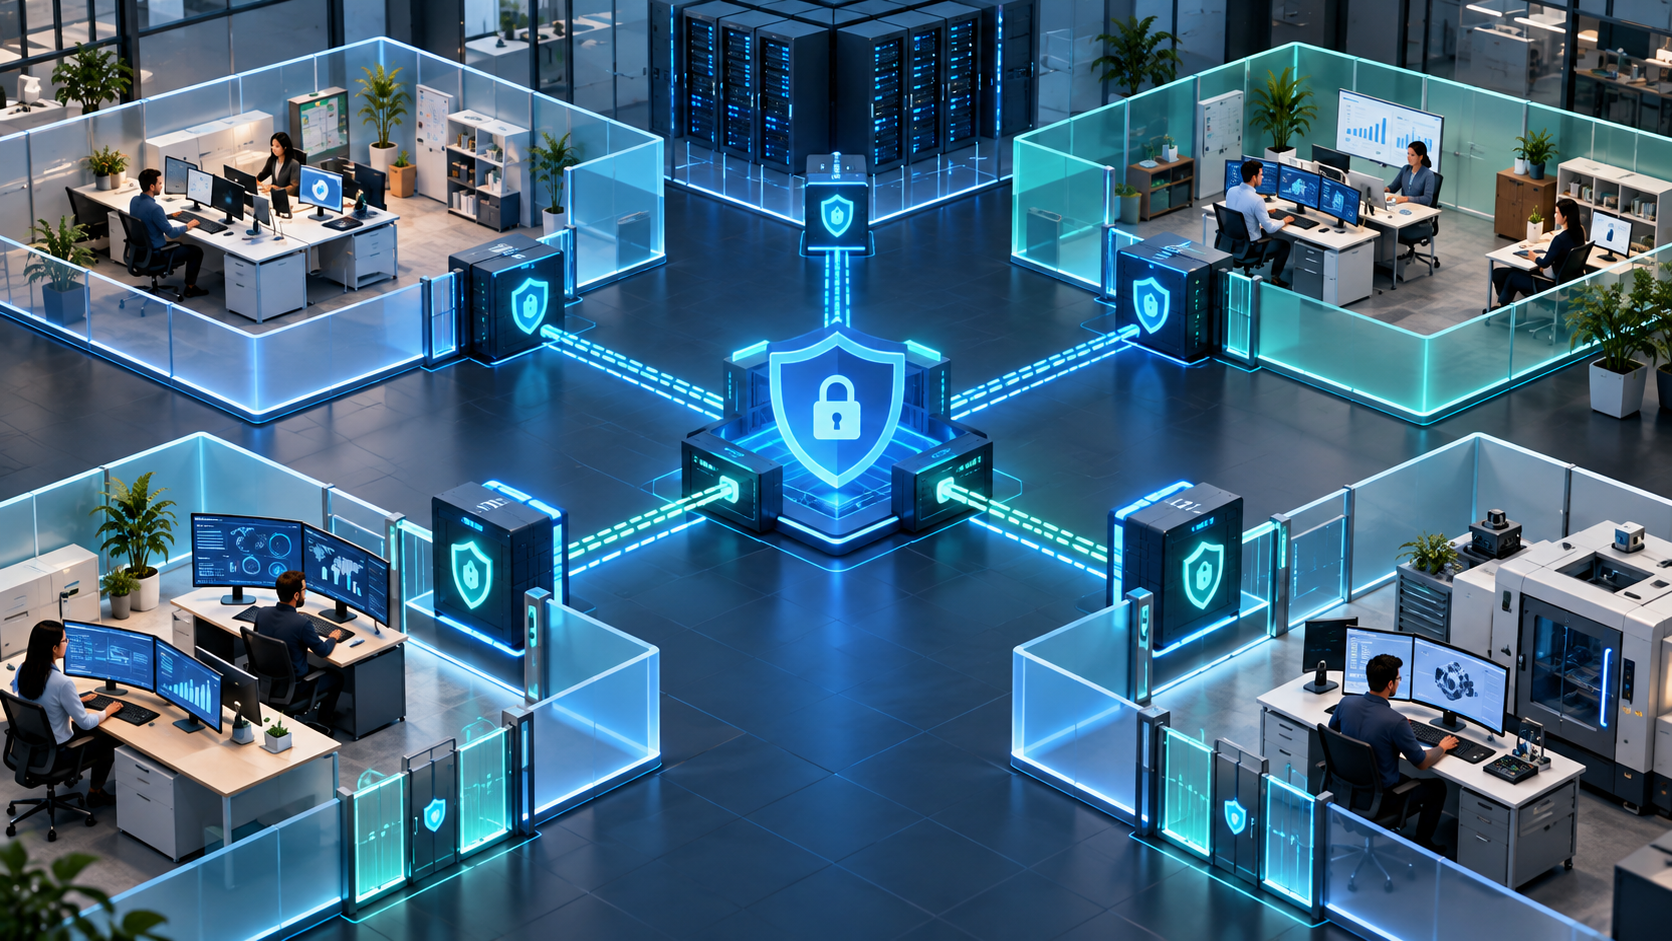
6. Segment sensitive resources
Do not allow one successful login to expose every system. Separate administrative, production, finance and customer-data environments where practical.
7. Re-evaluate access continuously
Zero trust is not “authenticate once and trust forever.” Sessions, devices and user behavior should be reviewed as conditions change.
8. Log important security events
Businesses need enough visibility to investigate suspicious authentication, administrator actions and access changes.
9. Remove dormant accounts quickly
Former staff, expired contractors and unused service accounts create unnecessary attack surface.
10. Protect data independently of network location
Sensitive information should remain protected even when accessed through cloud platforms or remote environments.
A Practical Zero Trust Roadmap for Small Businesses
Stage 1: Inventory identities and critical resources
List employees, contractors, administrators, devices, cloud applications, hosting accounts, finance systems, customer-data stores and other important resources.
Stage 2: Strengthen authentication
Enable MFA or passkeys. Remove shared administrator accounts. Protect recovery methods and ensure business email is secured.
Our Microsoft 365 security checklist covers several identity and administrative controls useful for organizations using Microsoft cloud services.
Stage 3: Apply least privilege
Review who can access what. Remove unnecessary administrator roles and separate business functions where possible.
Stage 4: Improve device security
Require supported operating systems, current security updates, disk encryption where appropriate and endpoint protection.
Stage 5: Replace broad network access
Traditional VPN access may grant a user visibility into more of a network than necessary. Identity-aware access and application-specific controls can reduce that exposure.
Our business VPN guide explains the difference between conventional VPN connectivity and more granular zero-trust approaches.
Stage 6: Monitor and review
Track suspicious sign-ins, privilege changes, unusual access and inactive accounts. Periodically review whether access rights are still justified.
Zero Trust vs Traditional VPN
| Area | Traditional VPN | Zero trust approach |
|---|---|---|
| Trust model | Often trusts the connected user/network more broadly | Verifies access to specific resources |
| Identity | User login may be the primary control | User, device and context can influence access |
| Access scope | May expose network segments | Aims for least-privilege resource access |
| Remote work | Extends private network connectivity | Protects resources regardless of location |
Zero Trust and Microsoft 365
Small businesses using Microsoft 365 can apply zero-trust concepts through identity controls, conditional access where licensed, strong MFA, restricted administrator roles, device management, session policies and logging.
Zero Trust and SaaS Applications
Each SaaS application should have a defined owner, approved users, appropriate permissions and a removal process. Single sign-on can simplify identity management, but it also makes the identity provider a critical security dependency.
Zero Trust and Contractors
Contractors often need access for a limited project. Create individual accounts, grant only required permissions, set an expiration date where possible and remove access immediately when the engagement ends.
Zero Trust and Website Administration
WordPress, hosting, DNS and domain-registrar accounts should follow the same principles. Limit administrator access, secure devices, require strong authentication and monitor for unexpected account changes.
Use our website security checklist to review the broader website-control baseline.
Common Zero Trust Mistakes
- Buying a product before identifying critical resources.
- Leaving shared administrator accounts in place.
- Requiring MFA but ignoring compromised devices.
- Granting permanent access to contractors.
- Using a VPN as proof that a user should be broadly trusted.
- Failing to monitor privileged activity.
- Keeping unused SaaS accounts active.
Zero Trust Implementation Checklist
- Inventory users, devices, applications and critical data.
- Require strong authentication.
- Separate administrator identities.
- Apply least privilege.
- Secure and patch endpoints.
- Reduce broad network access.
- Review contractors and service accounts.
- Monitor authentication and privilege changes.
- Remove inactive accounts.
- Document access-review responsibilities.
Use Security Visibility and Search Visibility Together
Security teams focus on controlling access; marketing teams focus on helping customers find the business. Website owners can use CBOOMARANK to review SEO performance, analyze competitors and identify keyword and backlink opportunities.
Explore available plans at CBOOMARANK pricing.
Frequently Asked Questions
Is zero trust only for large enterprises?
No. A full enterprise architecture may be complex, but small businesses can apply zero-trust principles such as strong identity verification, least privilege, device security, separate administrator accounts and continuous access review.
Does zero trust replace a VPN?
Not necessarily. Some organizations continue to use VPNs for specific connectivity needs while applying more granular identity- and resource-based controls around sensitive systems.
What should a small business implement first?
Start with critical identities and resources: business email, administrators, finance, cloud platforms, hosting and customer data.
Final Takeaway
Zero trust is most useful when treated as a disciplined access strategy rather than a product label. Small businesses can make meaningful progress by verifying identities, protecting devices, limiting privileges and granting access only to the resources people genuinely need.